Buy jpss.eu ?
We are moving the project
jpss.eu .
Are you interested in purchasing the domain
jpss.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy jpss.eu ?
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **


Similar search terms for TPM
Top-Angebote
Products related to TPM:
-
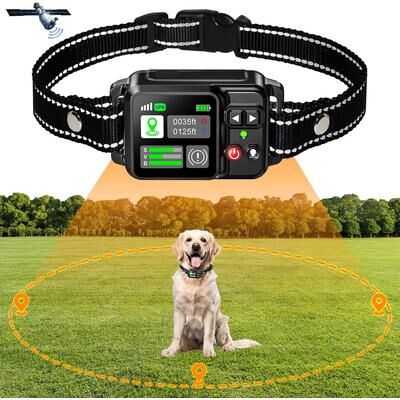
PetsAreLife GPS Wireless Dog Fencing System, Electric Dog Fence With GPS Electric Satellite Technology, Electric Pet Fencing System GPS Wireless Dog Fencing System, Electric Dog Fence With GPS Electric Satellite Technology, Electric Pet Fencing SystemKeep your best friend safe, happy, and free to roamwithout ever worrying about escapes. Our GPS Wireless Dog Fencing System combines cuttingedge satellite positioning with reliable electric borders to give you complete control over your pets play...114,99 $*Shipping: 0,00 $Secure redirect to the provider
-
Research-powered Eye Duo - Skincare Kit Charlotte Tilbury 3233 Charlotte's Research-powered Eye Duo Size:Darlings, unlock the secret to eyes that appear brighter, depuffed, smoother and younger with my Research-Powered Eye Duo! This CharlotteTilbury.com EXCLUSIVE skincare duo includes:94,05 £*Shipping: 0,00 £Secure redirect to the provider



-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
Top-Angebote
Products related to TPM:
-
Asus TPM-SPI V2.0 Security TPM ModuleThe ASUS TPM SPI V2.0 Security Module is designed to enhance computer security by providing dedicated hardware based protection for compatible systems. It helps securely store encryption keys, digital certificates, passwords and other sensitive information. Using a 14-1 pin SPI interface, the module is designed for compatible ASUS motherboards and systems that support the TPM SPI standard. It provides a dedicated Trusted Platform Module solution for systems requiring hardware based security features. The module uses the Nuvoton NPCT750 security chip and complies with the Trusted Computing Group TPM 2.0 specification. This allows it to support security functions that help protect platform integrity and digital identities. Security certifications include Common Criteria EAL4+ and FIPS 140-2. The module also meets CE and RoHS compliance requirements, providing a certified solution for compatible computing platforms. The ASUS TPM SPI V2.0 is a compact internal security accessory designed for straightforward motherboard integration. Before installation, compatibility should be checked carefully because TPM SPI and TPM LPC modules use different pin definitions and are not interchangeable.15,99 £*Shipping: 0,00 £Secure redirect to the provider
-
The Handy Homestead GPS Wireless Dog Fencing System Electric Pet Containment With Satellite Technology GPS Wireless Dog Fencing System Electric Pet Containment With Satellite TechnologyEnsure your dogs safety without the hassle of traditional fencing with our GPS dog fence system. Designed for pet owners who want a reliable, invisible barrier, this system uses advanced GPS Satellite Technology to create a customizable perimeter...109,97 $*Shipping: 0,00 $Secure redirect to the provider
-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
Similar search terms for TPM
-
PetsAreLife GPS Wireless Dog Fencing System, Electric Dog Fence With GPS Electric Satellite Technology, Electric Pet Fencing System GPS Wireless Dog Fencing System, Electric Dog Fence With GPS Electric Satellite Technology, Electric Pet Fencing SystemKeep your best friend safe, happy, and free to roamwithout ever worrying about escapes. Our GPS Wireless Dog Fencing System combines cuttingedge satellite positioning with reliable electric borders to give you complete control over your pets play...114,99 $*Shipping: 0,00 $Secure redirect to the provider
-
Research-powered Eye Duo - Skincare Kit Charlotte Tilbury 3233 Charlotte's Research-powered Eye Duo Size:Darlings, unlock the secret to eyes that appear brighter, depuffed, smoother and younger with my Research-Powered Eye Duo! This CharlotteTilbury.com EXCLUSIVE skincare duo includes:94,05 £*Shipping: 0,00 £Secure redirect to the provider
-
Motorola Defy Satellite Link Two-Way Satellite Messenger with SOS (BM3A01) - BlackStay connected wherever your adventures take you with the Motorola Defy Satellite Link BM3A01. Designed for hikers, campers, travellers, off-road enthusiasts, and outdoor professionals, this compact and rugged satellite communicator enables two-way satellite messaging, location sharing, and SOS emergency assistance, even in areas without mobile network coverage. Pairing seamlessly with compatible Android and iOS smartphones via Bluetooth, it extends your communication capabilities far beyond traditional cellular networks. Built to withstand harsh environments, the Motorola Defy Satellite Link features a rugged IP68-rated and MIL-STD-810H certified design, offering excellent resistance to water, dust, drops, and extreme temperatures. The integrated GPS technology allows you to share your location with family, friends, or colleagues, providing extra peace of mind during outdoor adventures or remote work. The dedicated SOS button offers instant access to emergency response services (subscription required), while the rechargeable battery delivers multiple days of operation on a single charge. Lightweight, compact, and easy to carry, the Motorola Defy Satellite Link is an essential companion for anyone who needs reliable communication and safety when venturing beyond cellular coverage.69,49 £*Shipping: 0,00 £Secure redirect to the provider
-
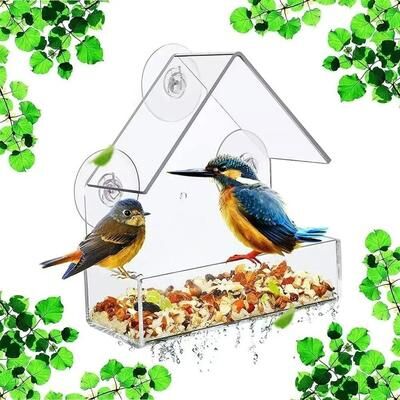
Uplift Essentials Bird Feeder High Definition Wildlife Observation Bird Feeder High Definition Wildlife Observation"Experience the beauty of nature from the comfort of your living room with the CrystalView Window Bird Feeder. Crafted from ultraclear, heavyduty acrylic, this ""bird house"" feeder offers an unobstructed, 360 view of your favorite local birds as they..."31,97 $*Shipping: 0,00 $Secure redirect to the provider
-
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
Which one fits with TPM 20?
TPM 2.0 (Trusted Platform Module 2.0) is a hardware-based security solution that is designed to provide a secure foundation for various computing devices. It is typically integrated into the motherboard of a device and provides features such as secure boot, cryptographic key generation and storage, and hardware-based device authentication. TPM 2.0 is designed to enhance the security of devices and protect against various types of attacks, making it a suitable choice for organizations and individuals looking to secure their computing infrastructure. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.